Taking projects from Q4 2026
We fix the IT that quietly costs you money.
Endpoint fleets, identity platforms and the operational workflows around
them - assessed, rebuilt, migrated and documented by two senior engineers. Based in
Prague, working with clients worldwide.
24+Years of experience combined
3,000+Endpoints managed
~5M USDClient cost removed
5Languages spoken
What we do
Six things we get called in for.
Usually because something is growing faster than the IT that supports
it, or because an audit deadline just became real.
Endpoint & device management
Zero-touch enrolment, configuration baselines, patch and compliance policy across
macOS and Windows fleets - built so support tickets go down, not up.
Identity & access
SSO, MFA, device trust and joiner-mover-leaver automation. Access that auditors
accept and employees stop working around.
Platform migrations
MDM transitions, tenant moves and storage consolidations executed on a fixed
cut-over plan, with rollback defined before the first device is touched.
Automation & scripting
The manual work your team repeats every week, turned into scripts, workflows and
API integrations that fail loudly instead of silently.
IT operations maturity
Ticket analysis, SOPs, escalation paths and onboarding flows - so the same
incident stops being solved five different ways.
Security & compliance readiness
Hardening, data classification, evidence collection and the documentation
certification bodies actually ask for.
Selected work
Anonymised, but the numbers are real.
Clients are described by industry and scale. Everything else is exactly
what happened.
Physical security company · ongoing engagement
Full IT stack assessment and improvement roadmap
- Situation
- A physical security company wanted an independent read on its IT stack -
Jamf Pro, Google Workspace, Azure, JumpCloud, SentinelOne and Box, plus the
inventory, SSO, automation and account/hardware lifecycle processes tying it
together - before deciding what to fix first.
- What we did
- Audited every system in scope, mapped the weak points and the risk behind
each one, then handed their IT team a prioritised improvement plan and are
guiding them through implementing it - advisory, not hands-on-keyboard.
- Impact
- TODO(content) - engagement is ongoing, update once improvements are implemented
Systems in scope
6 platforms
Engagement
Assessment + guided implementation
Status
Ongoing
Cybersecurity company · Prague office · 2026
ISO 27001 audit prep
- Situation
- The Prague office has an upcoming ISO 27001 audit, and needed its compliance
documentation and evidence trail brought up to standard beforehand.
- What we did
- Both of us are running the compliance preparations together - closing
documentation gaps, tightening evidence collection, and getting the processes
audit-ready.
- Impact
- TODO(content) - audit is upcoming, update once the outcome is confirmed
Digital agency · 43 shared drives · 2022–2023
Large-scale Box data migration
- Situation
- 43 shared drives - around 20 TB of data including full version history - needed
to move to a new structure without losing history or breaking permissions.
- What we did
- Migrated the data with Box Shuttle, with mirrored root-folder and security-group
structures prepared ahead of the move.
- Impact
- 20.5 TB migrated across 43 shared drives, full version history preserved.
Data migrated
20.5 TB
Shared drives
43
Version history
Preserved
Digital agency · 2 sites · 2021–2022
TISAX AL3 certification under a hard client deadline
- Situation
- Their largest customer required AL3 labels for prototype and confidential data.
Missing the deadline meant losing the contract and 75 internal roles with it.
- What we did
- Split the programme into documentation, process and people. Wrote the data
classification and handling policy, rebuilt external sharing controls, automated
vendor and client account requests with time-bound approval, then trained every
employee on what changed and why. The auditor tested our endpoint, identity and
network security configuration in detail, plus HR/legal documentation and physical
site security.
- Impact
- Both sites passed at the strictest level, with a single minor exception flagged
for a subcontractor's onboarding status, resolved on a temporary-label basis while
it closed out. The auditor noted the standard of automation was higher than
expected for a company of this size. Operations continued uninterrupted, and the
automated request workflow ended up saving time rather than costing it.
Certification
Not assessed
AL3 passed
Contract at risk
Retained
Duration
12 months
Findings
1 minor, resolved
Digital agency · 180 TB · 8 weeks · 2020
Cloud storage consolidation on a two-month deadline
- Situation
- Renewal for a legacy file-storage platform was due in January and cash flow
couldn't cover it. No ownership documentation existed - everyone had access to
everything.
- What we did
- Reconstructed data ownership from access logs, confirmed it with team managers,
then rebuilt the permission model per department. Ran the transfer with
throttled sync jobs, folder-by-folder cut-over, read-only freezes and a final
delta sync before handover.
- Impact
- Migration finished before the renewal date. Only the 80 TB actually in use was
moved; the rest went to cheap archive storage, avoiding a licence tier upgrade.
Annual licensing
$60,000
$0
Transfer budget
$2,000 allocated
under $500 spent
Access model
Everyone, everything
Per-department
Global enterprise · multi-region helpdesk · 2015–2019
Root-cause analysis on a growing ticket queue
- Situation
- Ticket volume in several categories was climbing and the proposed fix was
hiring more agents.
- What we did
- Pulled six months of tickets and drilled into the recurring categories. Found
the same issues being solved five different ways with almost no shared
documentation. Built a reviewed SOP repository, automated the common fixes and
pushed the preventable ones out as policy.
- Impact
- Fewer tickets, resolved faster, without adding headcount.
Ticket volume
−15 to 20%
Average resolution
17 min
8 min
Extra headcount
None
How we work
Four steps, and you can stop after any of them.
Assess
We look at the fleet, the identity stack and the tickets. You get findings ranked
by cost and risk - useful even if you never hire us again.
Design
A target state that fits your team size and budget, with the migration path,
rollback plan and what stays manual on purpose.
Deliver
Pilot group first, then staged rollout with a defined cut-over date and
communication your users will actually read.
Hand over
Runbooks, admin training and a recorded walkthrough. The goal is that you don't
need us on retainer.
Who you'll work with
Two engineers. No account managers.
The people who scope the work are the people who do it.
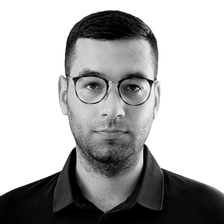
Chazem Al-Daken
Endpoint & identity architect
Nine-plus years running macOS and Windows fleets at scale in cybersecurity and
other enterprise-grade environments. Currently leads endpoint management strategy
and operations for a 3,000+ device estate at SentinelOne, running point on MDM
migrations, IdP integration and lifecycle automation end to end - not just the
plan, the execution. Jamf-certified across three of the four tiers, deep in Okta
device trust.
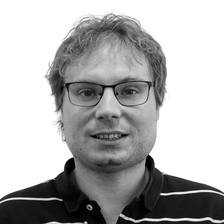
Jan Bakalar
IT process & automation consultant
Fifteen years turning manual business processes into automated workflows, from
IT helpdesk to endpoint strategy and compliance programmes. Now IT team manager
at SentinelOne, leading a 2,300-device MDM migration and ISO 27001 audit prep,
alongside a VDI rollout that cut global hardware costs by $5M. Background in
organisational psychology - which is why the rollouts land.